
What a Reliable CI/CD Pipeline Should Include
A practical CI/CD pipeline setup checklist covering build, tests, artifact promotion, secrets, deployment checks and rollback.
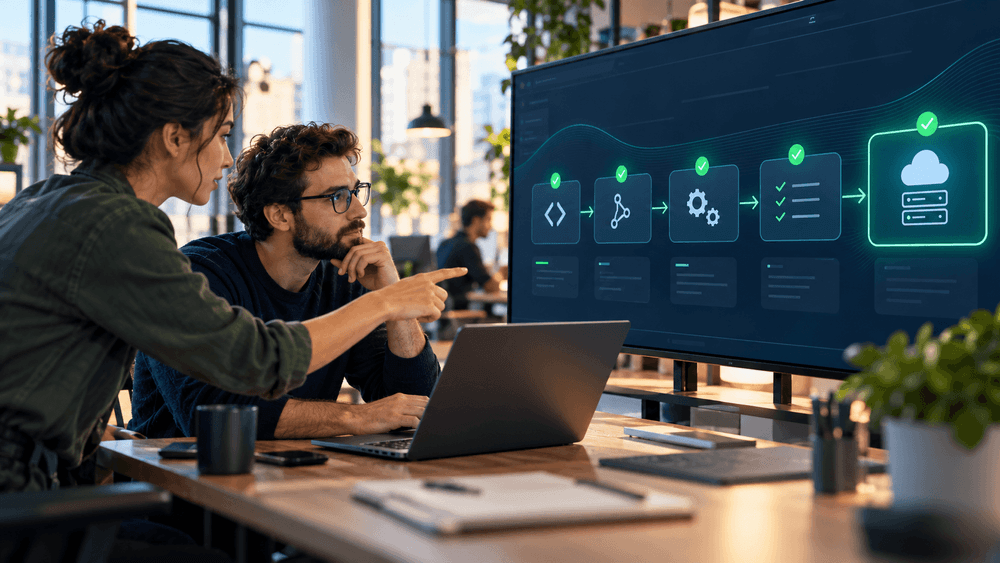
A CI/CD pipeline should make a software release repeatable and visible. It should answer straightforward questions: Which code was built? Which tests ran? Which artifact reached staging and production? Who approved the release, and what will happen if the service fails its checks?
The best pipeline is not necessarily the one with the most stages. It is the one that catches useful problems early, removes avoidable manual work and gives the team a dependable route to production.
Understand the Three Jobs in the Pipeline
Continuous integration (CI) brings code changes together and runs checks such as compilation, tests and static analysis. Continuous delivery keeps a tested version ready to release. Continuous deployment goes a step further by automatically sending an approved change to production when its checks pass. A team can adopt CI and delivery without automating every production decision.
In GitLab's pipeline model, jobs perform tasks and stages control their sequence. Other systems use different names, but the basic flow is similar: trigger, build, test, package, deploy and verify. Start with the gates that protect your application, then add complexity only where it solves a real failure mode.
Build Once and Promote the Same Artifact
The pipeline should create a versioned package or container image from a known commit. Record the commit, build time and dependencies. Avoid rebuilding the application separately for staging and production; those builds can differ even when the source commit is the same.
For a containerized API, the pipeline can build an image, run tests and publish it to a registry. The production deployment then refers to that tested image version. A private registry such as Harbor can add access controls and vulnerability scanning, but the process still needs a rule for how findings are reviewed and when an image may proceed. See our Docker production checklist for the application side of this work.
Put Fast Checks Before Expensive Ones
Compile and unit-test early, then run broader integration and security checks as the build progresses. A check that regularly takes too long or fails for reasons unrelated to the change will be ignored or bypassed. Review flaky tests and track how often a failure represents a real defect.
The pipeline also needs safe access to environments. Store secrets in an appropriate secret manager or CI variable mechanism, limit who may trigger production jobs and prefer short-lived credentials where the platform supports them. GitLab's CI/CD hardening recommendations highlight why production environments and pipeline permissions need explicit restrictions.
Verify What Happened After Deployment
A deploy step reports that the platform accepted an update. It does not prove that the application is useful. Add health and smoke checks for the paths customers depend on, such as authentication or a core transaction. Record the result beside the release version so an operator can connect an incident to a change.
Decide in advance whether a failed check should pause, roll back or call a person. The answer depends on the application and the type of change. A Kubernetes rolling update can replace running instances gradually, while a database migration may require a separate compatibility plan. Our rollback guide explains those limits.
Adopt the Pipeline in Manageable Steps
Begin with one service and a small set of reliable checks. Make its build reproducible, automate deployment to a non-production environment and document the production release. Once those steps work, add promotion, approval and automated recovery where appropriate. Teams that already use GitLab, Harbor and Argo CD can separate CI from cluster reconciliation; our GitOps pipeline guide shows how those roles fit together.
A practical pipeline example
Imagine a small customer portal with a web application and API. A merge request runs linting, unit tests and a container build. On merge, the pipeline publishes one versioned image, deploys it to staging and runs a login and API smoke test. A production approval then promotes the tested version; a final check verifies that users can reach the portal. The deployment record links the commit, image, approver and result.
The design does not need every test on every keystroke. Fast checks can run on each merge request, with slower end-to-end tests at a deliberate stage. What matters is that the team understands which failures block a release and which results are advisory. A failing test that is routinely ignored is weaker protection than a smaller set of trusted checks.
Before calling a pipeline complete, ask another engineer to find the version running in production, trace it to a commit, see the test result and follow the rollback procedure. If those tasks are difficult, the pipeline still has a visibility or ownership gap. Codativity can help design and implement a release path that your team can operate confidently.

6/11/2026
Contact Us
701, Opal Tower Business Bay, Dubai United Arab Emirates
P.O.Box 126732

Let's Work Together
© 2016 - 2026 Codativity Software Solutions. All Rights Reserved.